Understanding Rashtml5gateway: Bridging Legacy Systems and Modern Web Access
In the evolving landscape of enterprise IT, the challenge of providing secure, seamless access to legacy applications remains a priority. Rashtml5gateway represents a technical approach to solving this problem by leveraging HTML5 to bridge the gap between traditional remote access protocols and modern web browsers. By eliminating the need for thick clients or complex VPN installations, this gateway architecture allows users to access remote workspaces, identity managers, and specialized software through a standard web interface.
What is an HTML5 Gateway?
An HTML5 gateway acts as an intermediary layer between a client's web browser and a backend server or remote desktop environment. Historically, remote access required specific software—such as RDP (Remote Desktop Protocol) or VNC clients—to be installed on the end-user's machine. A gateway transforms these protocols into a stream that a browser can render using HTML5, CSS, and JavaScript.
The primary objective of implementing a solution like Rashtml5gateway is to provide clientless access. This means that as long as a user has a compatible web browser, they can interact with high-performance applications without worrying about operating system compatibility or local software dependencies.
Key Benefits of Web-Based Remote Access
Transitioning to an HTML5-based gateway offers several strategic advantages for organizations managing diverse software portfolios:
- Simplified Deployment: Administrators no longer need to push software updates to thousands of end-user devices. Updates are handled centrally at the gateway level.
- Enhanced Security: By keeping the remote session within the browser, the internal network remains shielded. The gateway acts as a controlled entry point, reducing the attack surface compared to traditional open VPNs.
- Cross-Platform Compatibility: Whether a user is on macOS, Linux, or Windows, the experience remains consistent because the heavy lifting is done on the server side.
- Improved User Experience: Users can access their workspace via a single URL, integrating identity management and single sign-on (SSO) for a streamlined login process.
Technical Implementation and Integration
Implementing a gateway requires a robust backend capable of handling session persistence and low-latency data streaming. Many modern implementations leverage frameworks that allow for AI-ready access layers or highly scalable microservices. For instance, using tools like Quarkus or similar Java-based frameworks helps build an access layer that can scale dynamically based on user demand.
Use Cases for Rashtml5gateway Architectures
The versatility of HTML5 gateways makes them ideal for several specific industry scenarios:
1. Specialized Engineering Software
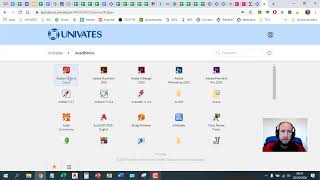
High-resource applications, such as AutoCAD or ArcGIS, typically require powerful hardware. By using a gateway, these applications can run on high-performance servers in a data center, while the user interacts with the software via a browser. This allows students and professionals to use professional-grade tools on low-spec laptops or tablets.
2. Remote Workspace Management
For organizations managing distributed teams, a gateway can transform the default web interface of a remote workspace. This allows IT managers to customize the identity manager and access controls, ensuring that users only see the applications relevant to their specific role.
3. Legacy Application Modernization
Many companies rely on "legacy" software that cannot be easily rewritten for the web. Instead of a costly total rewrite, a gateway provides a "web wrapper," making the old software accessible to modern users without changing the underlying code.
Security Considerations and Best Practices
While HTML5 gateways increase accessibility, they also introduce specific security challenges. To maintain a secure environment, administrators should implement the following:
- Multi-Factor Authentication (MFA): Since the gateway is accessible via a URL, MFA is essential to prevent unauthorized access via stolen credentials.
- Session Timeouts: To prevent "session hijacking," gateways should be configured to automatically terminate inactive connections.
- Encryption: All traffic between the browser